Проверка DNS-записей домена — утилита dig
Утилита dig позволяет отправлять на DNS-сервер запросы с заданными параметрами, чтобы узнать информацию обо всех или только о некоторых DNS-записях. Аналог dig — утилита nslookup: с её помощью тоже можно проверить DNS-записи домена.
Здесь вы можете воспользоваться онлайн-версией утилиты dig. Для этого достаточно указать нужный домен, а также дополнительные параметры (при необходимости).
— В поле «Домен» введите адрес, для которого вы хотите отобразить DNS-записи. — В выпадающем списке «Тип записи» выберите нужный тип DNS-записи (по умолчанию отображаются все доступные записи). — В поле «DNS сервер» укажите конкретный DNS-сервер, для которого вы хотите проверить DNS-записи (опционально).
Если вы хотите получить подробное отображение пути следования информации в системе DNS, отметьте галочку «С трассировкой». Для отображения информации в текстовом виде отметьте галочку «Текстовый ответ».
Проверка A-записи: чтобы узнать IPv4-адрес домена, в выпадающем списке «Тип записи» выберите «A».
Проверка AAAA-записи: для информации о IPv6-адресе домена в выпадающем списке «Тип записи» выберите «AAAA».
Проверка NS-записи: для получения онлайн-теста DNS-серверов домена в выпадающем списке «Тип записи» выберите «ANY».
Проверка MX-записи: чтобы узнать DNS MX-запись домена, в выпадающем списке «Тип записи» выберите «MX».
Проверка TXT-записи: чтобы посмотреть dig TXT-запись домена, в выпадающем списке «Тип записи» выберите «TXT».
Проверка SOA-записи: для проверки SOA-записи в выпадающем списке «Тип записи» выберите «SOA».
CNAME DNS check — чтобы узнать CNAME-запись домена, в выпадающем списке «Тип записи» выберите «CNAME».
Вам может быть интересно
- Хостинг WordPress
- Хостинг для 1C-Битрикс
- Конструктор Website builder
- Создание сайта на REG.Site
- Облачные серверы
- VPS на Windows
- Подобрать SSL-сертификат
- SSL-сертификаты GlobalSign
- Конфигуратор сервера
- Дешёвые серверы
Сервис проверки DNS-записи домена от REG.RU
Утилита dig (сокращение от «domain information groper») позволяет проверить записи DNS домена. На этой странице вы можете узнать DNS-информацию об ответах серверов имён и отобразить все основные записи домена с помощью онлайн-инструмента dig с простым графическим интерфейсом.
DNS (Domain Name System) — это глобальная система для преобразования доменных имён в IP-адреса сайтов. Когда пользователь пытается получить доступ к веб-адресу, например example.com, его веб-браузер или приложение выполняет запрос к DNS-серверу, передавая ему название сайта (имя хоста). DNS-сервер преобразует имя хоста в числовой IP-адрес (DNS to IP), к которому веб-браузер может подключиться.
Но одному домену могут соответствовать несколько IP-адресов, например один — для сайта, а другой — для почтового сервера. Все взаимосвязи между доменом и IP-адресами прописаны в специальном файле на DNS-сервере — файле DNS-зоны, который содержит различные типы записей.
A-запись — хранит имя хоста и соответствующий ему адрес IPv4.
AAAA-запись — хранит имя хоста и соответствующий ему адрес IPv6.
NS-запись — предоставляет адреса DNS-серверов домена.
MX-запись — указывает SMTP-сервер электронной почты для домена.
TXT-запись — обычно содержит текстовые примечания или машиночитаемые данные, например подтверждение права собственности на сайт, подпись DKIM, идентификацию DMARC и так далее.
SOA-запись — указывает основной DNS-сервер, контактные данные администратора домена, серийный номер файлы DNS-зоны и информацию о частоте запросов, проверяющих обновления DNS-записей.
CNAME-запись — используется для псевдонимов, например, при перенаправлении адреса с «www» на адрес без «www».
Как посмотреть TXT-записи домена?
Сделал домену TXT-записи, а как их посмотреть?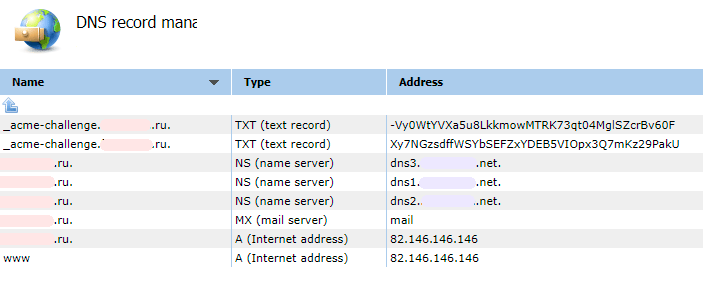
Я посмотрел на https://www.reg.ru/nettools/dig для этого домена, показывает только A, MX10, NS и SOA
- Вопрос задан более трёх лет назад
- 14130 просмотров
Простой 5 комментариев
- Вконтакте


комманда в терминале
dig txt _acme-challenge.domain.ru
либо dig txt _acme-challenge.domain.ru +trace
- Вконтакте
- Вконтакте
Что-то если выбрать ANY он TXT не показывает вообще тоже. А если выбрать только TXT показывает:
Как проверить txt запись домена
TXT records can be configured by the owner of a domain name. They are used to store information in the DNS, which can be looked up by anyone. Each record type has a different purpose. TXT records are often used to verify domain ownership with third parties. A Sender Policy Framework (SPF) record can usually also be found with a TXT lookup. Learn more about TXT records.
TXT records are configured in DNS. But how can you look up these TXT records? That depends on the operating system you are using. Windows, Linux and Mac all have a different way of finding TXT records. The sections below contain instructions for each operating system.

How to lookup TXT records on Windows
To check the TXT records for a certain domain name on Windows, follow these steps:
-
Open a command prompt by navigating to
‘Type here to search’ →
nslookup -q=txt example.com and hit
How to lookup TXT records on Mac OS
To check the TXT records for a certain domain name on a Mac, follow these steps:
-
Open a terminal by entering
dig example.com txt and hit
How to lookup TXT records on Linux
To check the TXT records for a certain domain name on Linux, follow these steps:
-
Open a terminal by entering
dig example.com txt and hit
How to find TXT records
To check the TXT records of a domain, follow these steps:
- Open the TXT lookup tool.

- Enter the domain name and hit
How to lookup other record types
There are other types of DNS records then just TXT. The most commonly used DNS record types are A, AAAA, CNAME, NS, TXT, MX and SOA. If you’d like to look up all records of these record types, you can do so with nslookup. Click any of the record types below to find DNS records for that specific record type.
How To Use Nslookup To Check DNS TXT Record
Being able to retrieve DNS TXT records is very useful in multiple scenarios. In this post we will look at checking the TXT domain verification record for Office 365 and also for the Sender protection Framework .
In addition to a MX record, we also have the option to prove domain ownership to Office 365 by using a TXT record. Why do we want to manually check for these Office 365 TXT records? Rather than blindly running the HCW and getting multiple failures, we can check that the correct record is present. This can help prevent the MaxUriReached: Same URI cannot be attached to different AppId on a single day error, which is discussed in KB 3027942.
When configuring the Sender Protection Framework (SPF), we need to create then add the SPF record into the external DNS zone file for a given domain. This is of type TXT nowadays. This allows external mail servers to consume the SPF record and make an intelligent decision based upon who the sender purports to be.
If we want to ensure that these records are correct, and available in public DNS we can use the nslookup tool. This is very useful if we do not have direct access to the DNS provider, as that may be owned by a different team within the organization.
As mentioned in How To Check Exchange Autodiscover SRV Record Using Nslookup, there are two ways to run nslookup – interactive and noninteractive. Noninteractive is good when you know that you only want to query a single piece of data. Interactive allows multiple queries using a single instance of nslookup, and options can be toggled on and off as needed.
Using Nslookup – NonInteractive
A quick query to check for TXT records in the Tailspintoys.ca domain could look like:
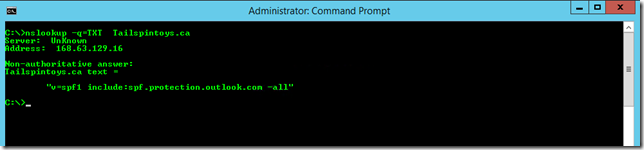
For the remaining examples, interactive mode will be used.
Using Nslookup To Quickly Check TXT Records
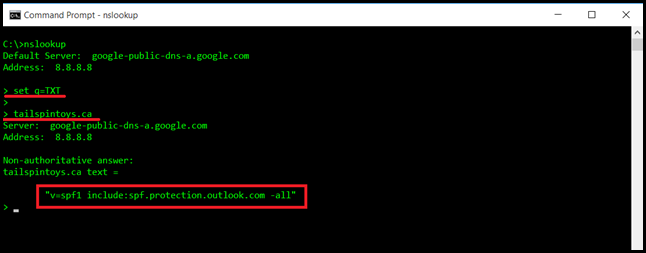
Launch nslookup in interactive mode. Then set the query type to be TXT:
Then we look for the TXT records for the given domain. In this case we are looking for TXT records present in the Tailspintoys.ca domain. The public Google DNS server was used so everyone can easily access it, and follow along with the steps in this post. You will find many open WiFi spots also using it.
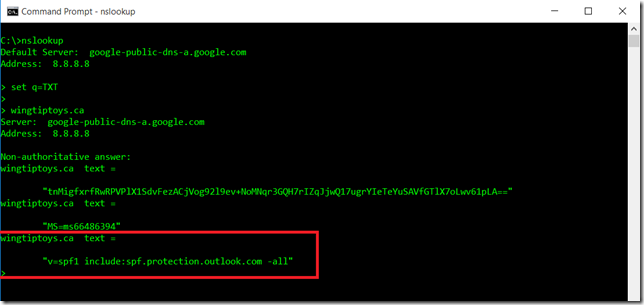
Repeating the test for the Wingtiptoys.ca domain shows additional TXT records that are present. There are three TXT records returned. The highlighted one is the SPF record, and the one immediately above that is the proof of domain ownership from Office 365.
Non-Authoritative Vs Authoritative
The eagle eyed reader will have noted that the queries returned are listed as non-authoritative. This is highlighted in the below red box.
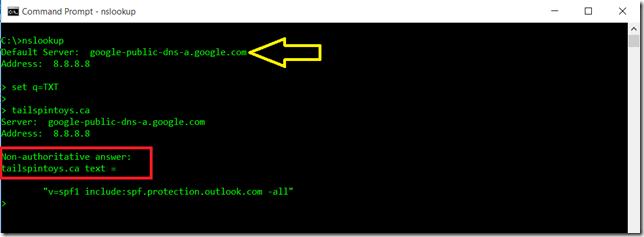
Why is this? The big yellow arrow above shows that we are querying against the Google DNS server. This DNS server is not authoritative for the zone, and has performed a recursive query on our behalf.
If we want to talk to the authoritative server directly, we can do so. We just need to know who that is. For redundancy purposes there should be at least two authoritative DNS servers specified in the DNS zone. While we can look for the SOA record, we should query for the Name Server (NS) record.
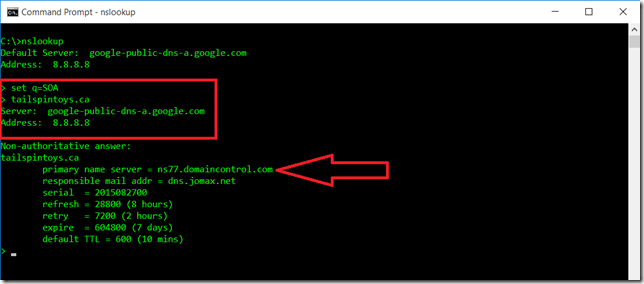
Note that the query type is now NS, which stands for “Name Server”.
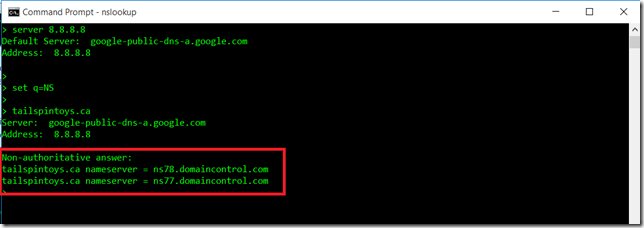
Now we know that for the tailspintoys.ca domain the two authoritative DNS servers are called ns78.domaincontrol.com and ns77.domaincontrol.com, we can query them directly. The IPv4 Addresses for those name servers are:
ns77.domaincontrol.com 216.69.185.49
ns78.domaincontrol.com 208.109.255.49
Note in the below screenshot, when we directly target those specific name servers, there is no mention of non-authoritative.
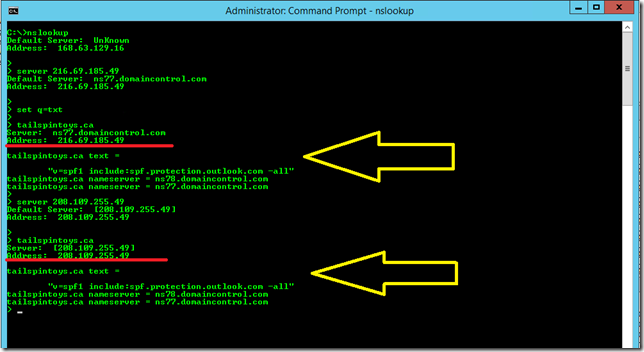
SPF Reference
For a quick reference, Microsoft has multiple SPF resources. The SPF wizard below helps to construct the content of your SPF record.
Update 17-11-2016 — Looks like the Microsoft SPF wizard has gone the way of the dinosaurs. Take a look at some of the other tools out there.
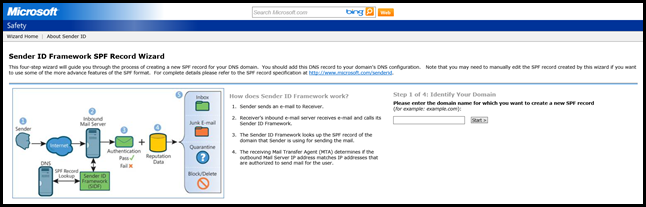
All SPF records contain three parts: the declaration that it is an SPF record, the domains & IP addresses that should be sending email, and an enforcement rule. You need all three in a valid SPF record. Here’s an example of the most common SPF record for Office 365:
TXT Name @ Values: v=spf1 include:spf.protection.outlook.com include:sharepointonline.com -all
Do not simply copy the above SPF record into your DNS zone. You need to plan to correctly implement SPF.
DNS Query Issues
Some issues that you might run into are listed below. It is not an exhaustive list.
Issue #1 – Use IPv4
One of my European colleagues noted they were having issues with NSlookup. They were seeing the below where every lookup was saying DNS request timed out.
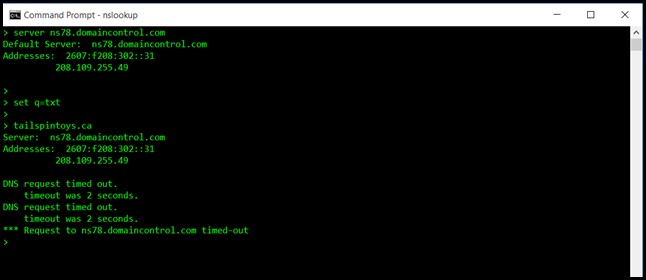
This was a weird one. Netmon never lies. But when I sniffed the traffic from my Windows 10 laptop and a Windows Server 2012 R2 VM, no packets were visible on the wire.
To resolve this, get the IPv4 Address of the DNS server and use that specifically in the server command. This is shown below.
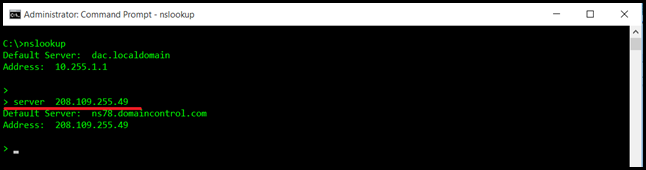
Issue #2 — Do Not Anger the Case Sensitivity Gods
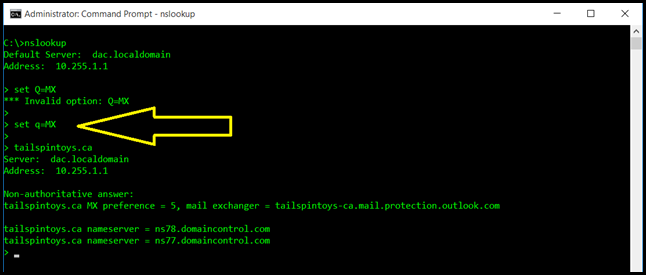
In Windows there are very few things that are case sensitive. Because of this we tend to get careless with case sensitivity. Take the below example when trying to set the query type:
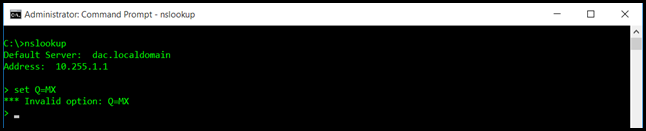
Note that the Q in query type is in capitals. This must be in lower case. Yes. Really.
The big yellow arrow (is it big enough??) shows that the working option is in lowercase.
Issue #3 – Beware Caching Devices
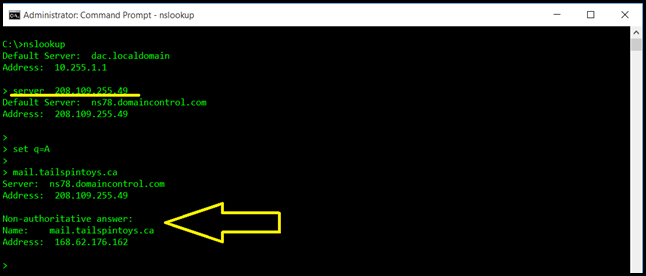
Multiple locations have implemented DNS caching devices that may or may not follow RFC standards. It is regrettable and quite common to find that some DNS caching device is quite happily ignoring the TTL on a DNS record and caching it for several days. Yes that does happen. Take the below example. This is written from some airport lounge in Canada that serves Glenfiddich. Though the amount of single malt consumed has nothing to do with any spelling mistak3s in this post!
In the below example we target the authoritative name server for the tailspintoys.ca domain. But note that we only get a non-authoritative answer.
Compare this to running exactly the same commands from a VM in Azure with no DNS shenanigans:
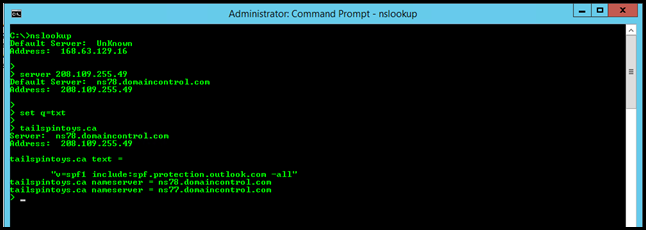
Those are indeed authoritative replies!
Issue #4 – Driving me Dotty
The devil is in the details, and also the dot sometimes. Note that in the below example, when we query for outlook.office365.com the query has the local computer’s DNS search suffix appended to it.
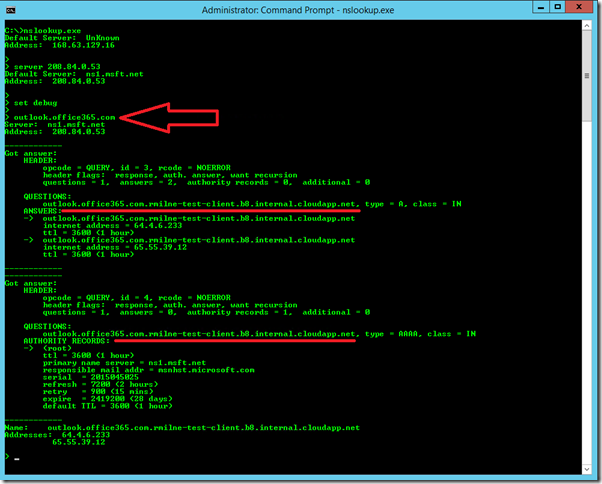
Compare the above queries (underlined in red) to the below screenshot. What is the difference? Note that the query below has a dot at the end of the query. This tells nslookup not to append the domain suffix.