Взлом Dead By Daylight
Открываем скаченный архив, далее заходим в папку "DBD".
— Открываем папку Config.
— Запускаем Exe
— В открывшемся окне нажимаем на Pak Creator
— В окне "Patch to .pak" Выбираем данный путь " Ваш диск где установлена игра:\SteamLibrary\steamapps\common\Dead by Daylight\DeadByDaylight\Content\Paks", в папке "Paks" выбираем файл с названием "pakchunk1-WindowsNoEditor.pak" и нажимаем Готов.
— Далее нажимаем на галочку во втором окне, и нажимаем START.
— В следующем окне нажимаем Jesus Config.
— Переходим во вкладку Config Creator.
— В первом окне FPS выкручиваем ползунок на максимум, во втором окне нажимаем на Fov 120.
— Закрываем программу.
—————————————————————————————————————————————————————————————-
— Открываем папку "bhvrSession + Market".
— Запускаем Cursed Market.exe.
— В открывшемся окне нажимаем START и соглашаемся со всплывшем окном.
— Заходим в игру до полного загружения.
— В программе нажимаем на кнопку "OBTAIN BHVRESSION".
— Копируем данный текст и сохраняем его.
На этом настройка закончена.
Для взлома необходимо ОБЯЗАТЕЛЬНО выполнить "Настройку Config".
— Заходим в папку "Osk +Rank"
— Открываем "XQDBD.exe"
— В открывшейся программе вставляем текст который мы скопировали в программе "Cursed Market.exe" и нажимаем Enter.
— Выбираем необходимый нам взлом и задаём параметры.
[1] — Показать кол-во валют на аккаунте.
[2] — Изменить кол-во кровавых очков (бладпоинтов) на аккаунте, максимум 1 миллион — 1.000.000
[3] — Изменить кол-во радужных осколков на аккаунте, так же повышает уровень разрыва. -ВНИМАНИЕ, РАНЕЕ БЫЛИ ВЫЯВЛЕНЫ СЛУЧАИ БЛОКИРОВКИ ЗА РАДУЖНЫЕ ОСКОЛКИ. НЕ ИСПОЛЬЗОВАТЬ.
[4] — Изменить ранг выжившего / маньяка.
[5] — Выйти из программы.
После того как все сделали выходим из программы.
Теперь можем зайти в игру и проверить наличие того что вы взломали, если что-то не получилось проверьте все ли пункты вы выполнили, начиная с "Настройки Config".
После каждого обновления игры вам нужно будет удалить 2 файла.
Первый файл находиться по пути " Ваш диск где установлена игра:\SteamLibrary\steamapps\common\Dead by Daylight\DeadByDaylight\Content\Paks", в папке "Paks" выбираем файл с названием "pakchunk1-WindowsNoEditor.pak".
Второй файл находиться по пути "AppData\Local\DeadByDaylight\Saved\Config\WindowsNoEditor" файл "Engine.ini".
После того как их удалили проверяем целостность файлов игры, и проделываем заново "Настройку Config" (Взламывать заново ничего не нужно).
На этом все, удачи!
Контакты:
Telegram — @HalFReaper
Discord — TAPEXX#0001
Dead By Daylight: Совет (Накрутка предметов, навыков, аддонов. Установка сейва) [5.1.1]

то
нажимаем на "Установить", откроется вкладка "Обход SSL", там нажимаем "Установить", либо другую кнопку, подробнее можно прочитать нажав на "Инфо" во вкладке "Обход SSL".
Теперь переходим к вкладе "bhvrsession".
Нажимаем "Запустить".

После соглашается с запросом установки сертификата.

И запускаем игру.
Во время загрузки игра закроется и сессия появится в программе, копируете ее.
НАКРУТКА
В DBD Tools открываем вкладку "Сохранения" вводим в bhvrsession полученную ранее сессию,
и жмем далее,
если все без ошибок, то станут доступны кнопки "Получить" и "Загрузить".
Сначала нужно сдампить профиль с серверов DBD, для этого жмем на "Получить"
После окончания процесса в папке с DBD Tools появится папка Profile в ней файл "FullProfile.txt", это и есть ваш сейв.
Также в папке будет "Backup.txt", он нужен для отката изменений.
(Если нужно вернуть старый сейв берете содержимое Backup и заменяете его в FullProfile, потом жмете "Загрузить");
Теперь нужно отредактировать сейв-файл, для этого открываем редактор, нажав
соответствующую кнопку в DBD Tools.
Как только зашли в программу выбираете свой FullProfile который вы получили из DBD Tools, нажатием на "File -> Open"

Теперь можете просто выбрать во вкладке Generator -> All 600 или любое другое число и у вас на всех персонажах будет всего по 600 , открыты все навыки, 50 лвл и 3 престиж.
Если нужно что-то конкретное, то выбирайте Custom Generator.

После того как вы закончили редактировать Fullprofile можно нажимать File -> Apply Changes в редакторе сохранений, и у вас будет сохранен ваш накрученный FullProfile.txt.

Теперь в DBD Tools нажимаем "Загрузить", подтверждаем клавишей "Enter".
Дожидаемся этой таблички:

Все. После перезахода в DBD у вас будет все накручено.
ЕСЛИ В ИГРУ ЧТО-ТО ДОБАВИЛОСЬ
Если что-то добавилось в игру, это будет обязаетльно добавлено и в редактор сохранений, как только вы увидите в DBD Tools доступное обновление для базы данных, можно нажать обновить и в редакторе уже будут новые предметы/перки/аддоны/подношения/персонажи. Далее делаете все по стандарту: Получили профиль, отредактировали, загрузили.
БЕСКОНЕЧНЫЙ ПЕРЕХВАТ СЕССИ
Если сертификат установился, но сессия не перехватывается, то нужно проверить состояние службы wpnservice. Для этого жмем правой кнопкой мыши по меню пуск -> Командая строка (Администратор). В окне командной строки пишем sc query wpnservice. Если STATE 1 : Stopped.

То пишем сюда же sc start wpnservice
Чтобы каждый раз не писать это, нужно внести некоторые изменения в реестр.
Для этого пишем в окно командой строки reg add "HKLM\SYSTEM\CurrentControlSet\Services\WpnService" /v Start /d 2 /t REG_DWORD /f
Все, теперь все должно работать.
Как узнать bhvrsession в dead by daylight
Last Achievements
Hi guys,
i want to release a new easiest method to get your bhvrSession in DBD
Status: Undetected (UD)
Follow the steps:
AmpyxTeam4Life
| ActionCrafted |
| View Public Profile |
| Find More Posts by ActionCrafted |
Last Achievements
Moderator note Due to the amount of embedded dlls (109) this was not thoroughly analyzed. Use at your own risk!

Last Achievements
AmpyxTeam4Life
| ActionCrafted |
| View Public Profile |
| Find More Posts by ActionCrafted |
Last Achievements
| mikangchan |
| View Public Profile |
| Find More Posts by mikangchan |
Last Achievements
AmpyxTeam4Life
| ActionCrafted |
| View Public Profile |
| Find More Posts by ActionCrafted |
Last Achievements
| nicedaantje |
| View Public Profile |
| Find More Posts by nicedaantje |
Last Achievements
Last Achievements
Last Achievements
AmpyxTeam4Life
| ActionCrafted |
| View Public Profile |
| Find More Posts by ActionCrafted |
Last Achievements
| PAHNTOMTOXX |
| View Public Profile |
| Find More Posts by PAHNTOMTOXX |
| TheDesiredHump |
| View Public Profile |
| Find More Posts by TheDesiredHump |
Last Achievements
Last Achievements
| 2510665011 |
| View Public Profile |
| Find More Posts by 2510665011 |
| JackRedplay |
| View Public Profile |
| Find More Posts by JackRedplay |
Last Achievements
Is it still undetectable ?? someone checked
Edit: After starting and pressing "Start proxy" I get the following information: [Error] SSL Bypass: unknown error
Breaking Dead by Daylight without process interaction
This article is a mirror of the previous release posted on the secret club blog.
For the past few months I’ve been looking into a game called Dead by Daylight which is protected by EasyAntiCheat. This game is unique in a special way and we’ll be exploring why. All these methods are already to be found on various types of forums and nothing is per se ground breaking. This is a guide about how I approached these things while shedding light into the inner workings of the actual cheats. Do not use this to get an advantage in the game.
Introduction#
What makes Dead by Daylight special? Dead by Daylight has a quite long record in terms of bugs and lazy coding. The game communicates with the game server using a REST API which is quite easy to reverse. As mentioned, the game is protected by EasyAntiCheat but in this case I tried to develop as many bypasses and cheats as possible without interacting with the game process at all.
Version 3.0.0#
Version 3.0.0 is quite famous in the particular cheating scene. It was one of the last versions that had no SSL pinning embedded, therefore making it easy to reverse the API. However, currently version 3.6.2 is out meaning that version 3.0.0 is no longer available to download through the store. Luckily, this isn’t stopping us thanks to Steam’s depot system which allows us to download any version of the game as long as we know the game specific IDs which can be looked up on SteamDB. To do this we have to run Steam with the “-console” flag and then enter download_depot 381210 381211 9043651681125706667 . Unfortunately, this isn’t working in the latest versions of Steam, but no worries, I’ll explain why. It turns out that the manifest file for this version is not available anymore. Luckily, Steam doesn’t really care about it as long as we just invert the check 🙂
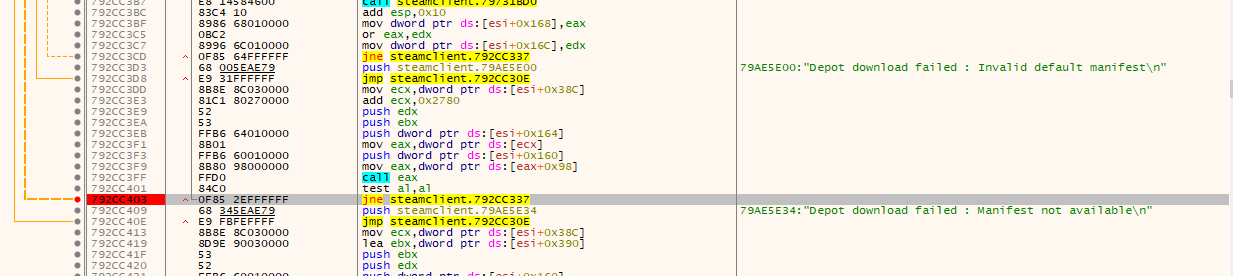
You can find an automated patcher on GitHub which you can run while Steam is running. Once the files are downloaded we can copy them over to Dead by Daylights installation path and fire up a sniffer like mitmdump or Fiddler.
Sniffing#
There’s 2 request of particular interest. The first one is a POST request which sends the current game version to the server to check whether there’s any:
This is easily bypassed by intercepting the traffic and changing the JSON body with the latest version IDs:
The response of this request contains a cookie called bhvrSession which we will need to further authenticate to the server.
One of the other important requests is the following GET request:
The request was stripped down to the most important part. The server returns all available versions that are allowed to log into the game server. This is easily bypassed by adding the identifiers for version 3.0.0 to the response body. Here’s a snippet from my script:
Unfortunately, Dead by Daylight introduced further checks based on locally generated tokens which are not present in this version of the game. This didn’t stop other cheaters to just embed the keys from the latest version into their own script and sending the values manually.
Of course I won’t let you sit around without knowing how some of the cheats handle this which is why I reversed one of them:
Yeah, that’s it. The keys are stored in settings.cfg . The last keys I had dumped from the cheat are:
Feel free to decrypt the newer versions and use his keys 🙂 Anyways, we wont do that. Lets upgrade to 3.6.2 and do it like the cool kids.
Version 3.6.2#
Upgrade as usual, you can do that by invalidating the files in Steam. Reinstalling works fine too. As mentioned before, Dead by Daylight has introduced SSL pinning, so how do we do it? Let’s take a deep dive into reverse engineering the game itself.
The true hero: Constants#
First things first, we need as much information of the target binary as possible. One of the first things I like to do is checking for strings:
Now we know they use libcurl version 7.55.1, probably a debug build. Even better! Let’s check the official documentation on how SSL certificates are handled. You can find the specific page here. Two constants are important: CURLOPT_SSL_VERIFYHOST and CURLOPT_SSL_VERIFYPEER . Let’s download the specific source code and open it up. Searching for those constants reveal an enum in curl.h :
Now let’s navigate to url.c where Curl_setopt is defined. Here’s a short excerpt of the function:
The possibilities are endless. We have a lot of inlined constants and a lot of string references at our disposal to find the function in memory. The function starts with the following assembly:
As we can see the register edx will contain the constant. Depending on what value is set it will branch to different code to apply the options passed to the function. We are primarily looking for the constants 0x40 and 0x51 . As we know from the original source code, the third argument contains the value, in this case it will be either true or false . The third register is r8 and contains a pointer to the memory holding the flag. We can use x64dbg’s conditional breakpoints to automatically patch memory on trigger:
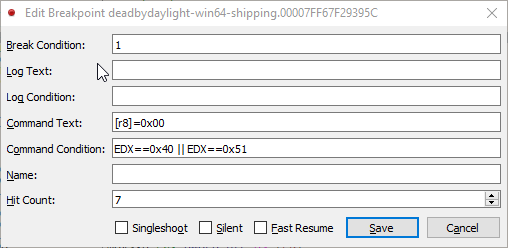
In the following image you can see that edx is set to 0x40 and that register r8 points to our patched value in memory.
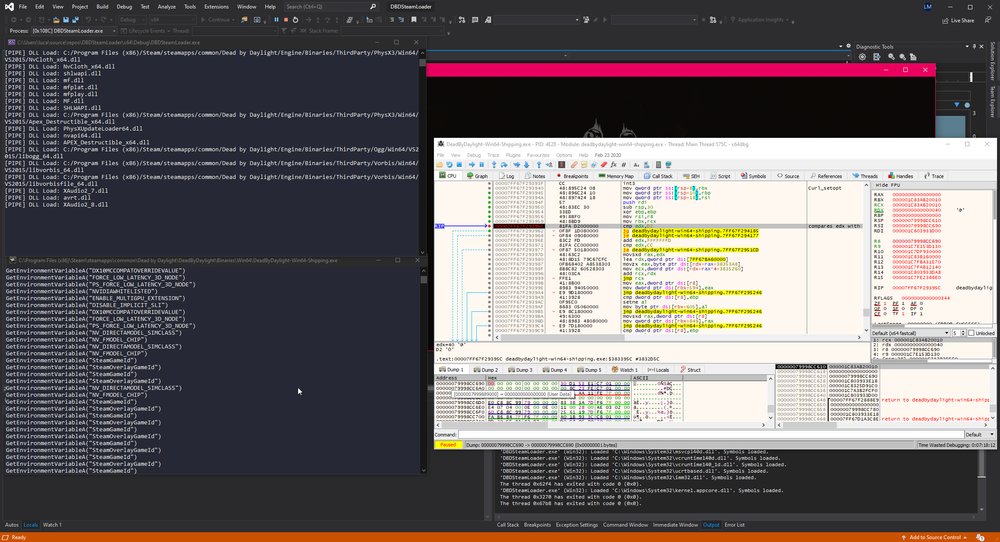
You may be wondering: “But we are touching the process?”. That’s right, we are and that’s why I’m gonna stop here 🙂 I’m currently working on an usermode emulator for EasyAntiCheat (which I’ve been using in the above screenshot), we will cover more about the debugging features in that article.
Experiments#
Looking back, I wish I had tried doing this before. Looking at Dead by Daylight’s track record it’s quite obvious that they must have messed up something trivial even in the latest version. The game uses Unreal Engine 4. All game assets are stored in so called “pak” files. Checking the strings of these files already reveals a whole lot of other information. Would you believe me if I told you Dead by Daylight doesn’t do any integrity checks on the “pak” files? Right. There’s 2 ways to approach this, either we give QuickBMS a shot or we use a hex editor. In this article we will be using the hex editor approach, doing it with QuickBMS is left as an exercise to the reader. The advantage would be that you can patch all configuration files and assets in the game, allowing you to get really close to a full wallhack. The file we will be editing is called pakchunk0-WindowsNoEditor.pak and hosts the main configuration files that are relevant for cheating purposes. Look for SSL and just erase the content to null bytes.
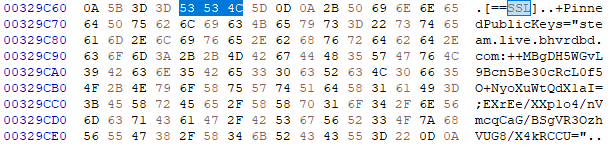
Here’s a dump of all the pinned keys that are being used:
Anyways, save the file, open up your proxy (in my case mitmweb) and run the game!
Sniff’n’Decrypt#
At this stage you should be able to see the requests. As you can see there’s also a new request to the endpoint clientVersion/check . Remember the keys I mentioned earlier? Those keys are sent to this endpoint, verifying our bhvrSession to be allowed to send further requests to the game server. However, we don’t have to worry about them anymore since the game does that for us without an issue.
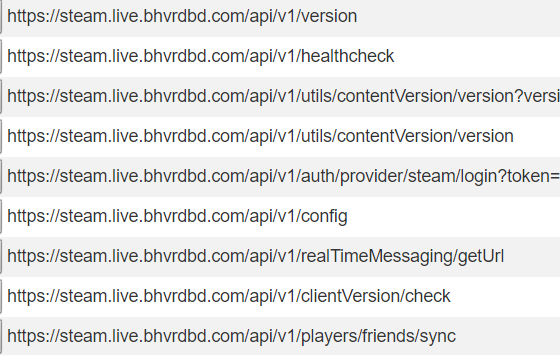
Eventually we will end up with a request to FullProfile/binary at this stage it’s a GET request which fetches the profile data of the current player.
This data contains the inventory, which is particularly interesting to cheat items. A very similar endpoint is used using a POST request which uploads the inventory. It is possible to decrypt the inventory, edit it, encrypt it and then send this to the server. This allows us to get whatever items we want, with whatever perks we want. To make things crystal clear, here’s how they decrypt the profile:
Encryption works the same way, just in reverse. This is also left as an exercise for the reader.
There’s also another request sent to and endpoint named /getUrl which provides you with a URL to a websocket endpoint. There’s a lot of information flowing through, some of it is in the game state 🙂 Unfortunately, only one client can be connected at a time, doesn’t stop you from proxying the websocket connection though. This is out of scope and is only mentioned as information, we will be doing this in an even funnier way. Nonetheless, sample code is provided here.
Predicting killers#
Recently some posts emerged of people polling the Dead by Daylight logfile to figure out the killer while being in the lobby. That’s all fun and stuff, but code like this just shouldn’t be written at all. Especially not if the author claims it to be for “learning purpose”:
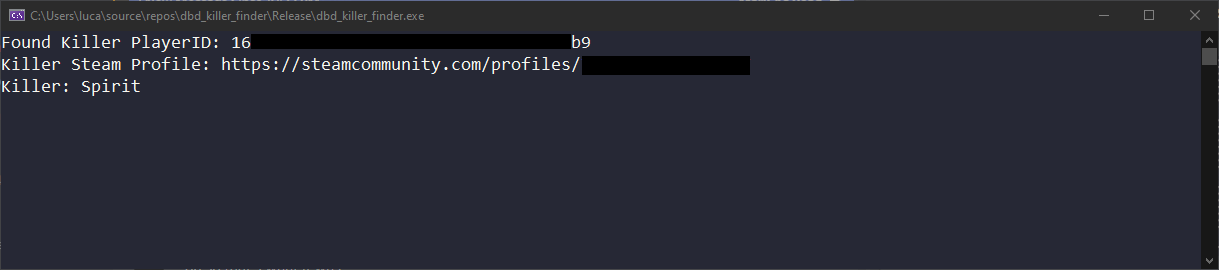
Let’s do it the right way. From our debugging session earlier you might have noticed that the game prints strings to the “Log” tab in x64dbg. This is because Windows redirects all debug strings that end up in DbgPrint to the debugger if one is attached. However, it’s actually possible to access these strings without a debugger and I’ve just recently reversed how to do so from DebugView. You can find the reversed project on my personal GitHub. The basic idea is to access Windows’ message buffer ( DBWIN_BUFFER ) and wait for certain events ( DBWIN_BUFFER_READY and DBWIN_DATA_READY ). This allows us to interact with the games logs in realtime without having to poll any text files and accidentally filter out old information which isn’t relevant. Utilizing very basic Regular Expressions we are able to determine the killer (even if he changes the character while being in the lobby which the original script can’t do!) and also his Steam profile. The options are endless! Here’s a broken down version of what is actually going on:
This code is just for demonstration purposes, you can find the project here.
Ranking up#
During my research I created a script (authenticator.py) that automates information dumping (such as bhvrSession ) and also decrypts the inventory. The data is being written in separate JSON files. Once the files are created you are free to run the scripts levelup.py and rankup.py. The scripts send basic POST requests to the endpoints /api/v1/ranks/pips and /api/v1/extensions/playerLevels/earnPlayerXp respectively. The needed JSON bodies are as follows (in the same order as above):
Final words#
To wrap things up I would like to say that there’s way more to explore and the code published can be improved in a lot of ways. I believe the most important take away is that debug events/strings can be really dangerous if used excessively. I believe that the general approaches and efforts from Behaviour are fine. However, some details still have room for improvement such as fixing their anticheat to check all game files. One more important note that I haven’t mentioned is the fact the pak files do not use an encryption key. Unreal Engine 4 has a feature to encrypt all game files with a specific key. Of course this can be reverse engineered but it makes creating cheats harder nonetheless. If there’s any open questions or feedback feel free to reach out to me on Twitter.