Некоторые замечания на тему VMware vSphere Security Permissions
Для предоставления доступа различным категориям пользователей к их виртуальным машинам, как правило, используется представление VM and Templates и система папок, на которые, собственно, и назначаются права. Однако, в некоторых случаях этого бывает недостаточно, поскольку для некоторых действий пользователь должен иметь права и на объекты среды, отсутствующие в отображении VM and Templates. Например, для добавления виртуального жёсткого диска или клонирования ВМ нужны права Datastore.Allocate Space или роль Datastore Consumer на объект Datastore или Datastore Cluster. А для возможности изменения сетевого интерфейса — права Network.Assign Network или роль Network Administrator на соответствующие портгруппы. Далее детальнее об этом и других нюансах назначения прав доступа в vSphere. Информация актуальна для версий vSphere 5.1 и 5.5.
Ввиду наличия различных представлений объектов инфраструктуры виртуализации, права доступа к некоторым объектам (VM, vApps) могут наследоваться от нескольких предков (например, VM folder и Resource Pool). что стоит иметь ввиду. Общая схема наследования представлена на рисунке:
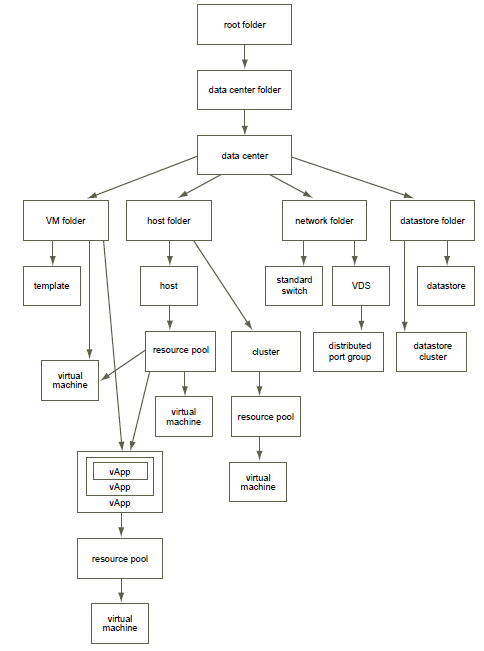
Соответственно, если кого-то нужно в правах ограничить, нужно убедиться, что отнятые в одном месте права не наследуются из другого объекта.
Помимо этого, можно столкнуться на практике, что человек, имеющий полномочия администратора на уровне рута, вдруг оказывается ограниченным пользовательскими правами на уровне конкретной папки. Дело в особенностях выбора действующих прав в ситуации наложения ролей. При предоставлении полномочий следует иметь их ввиду.
1) Права, выданные дочерним объектам игнорируют наследованные. Другими словами, если пользователь входит в группы vSphereAdmins и CitrixAdmins, при этом первая имеет права админа на уровне root, а вторая — VM User на уровне папки Citrix, то как раз получим ситуацию, описанную в вышеприведённом абзаце.
2) Права выданные на конкретного пользователя преобладают над правами, выданными на группу (если и те и другие выданы на один объект и пользователь входит в группу).
3) Если используются пользователи из AD или иных источников, отличных от встроенного каталога vCenter SSO, vCenter периодически проверяет наличие учётной записи поиском по имени. И если после назначения прав в vCenter, учётка была переименована или удалена, соответствующие ей права из vCenter удаляются. И если в случае удалённой учётки это даже хорошо, то в случае, если кто-то переименовал группу (группы), например в соответствие с новыми политиками именования в организации, это может привести к неблагоприятным последствиям.
4) vCenter SSO не наследует права вложенных групп, если их участники не входят в Identity Sources. Например, если домен AD не добавлен в Identity Sources, то группа Domain Admins этого домена не будет иметь никаких полномочий на vCenter, даже с учётом того, что она входит в local\Administrators сервера vCenter.
Немного рекомендаций лучших собаководов Best Practices по теме предоставления прав доступа.
- По возможности назначать права на группы, а не на конкретных пользователей. Контроль членства в группах можно делегировать и избавить себя от лишней работы. И даже если не делегировать, системой будет проще управлять.
- Выдавать права только там, где необходимо, тем, кому необходимо и с минимально необходимыми привилегиями. Опять же для понимания структуры, упрощения управления и должного контроля. Лучше сформировать заранее план необходимых полномочий и лиц, которым они нужны.
- Использовать папки для группировки объектов со схожими наборами прав. Папки, если что, можно создавать во всех представлениях, а не только в VM and Templates.
- Быть аккуратнее с предоставлением прав на корневом уровне. То есть на уровне самого vCenter в клиенте vSphere. Дело в том, что пользователь, имеющий права на этом уровне получает доступ не только к объектам инфраструктуры виртуализации, но и к управлению такими сущностями как лицензии, роли, интервалы сбора статистики, сессии и кастомизированные поля. А возможность модификации ролей может оказать влияние даже на те vCenter, на которые у пользователя вообще нет прав (при использовании Linked Mode).
- В большинстве случаев стоит включать наследование. Это гарантирует, что при добавлении нового объекта в определённую иерархию, пользователь, за него ответственный, получит к нему доступ.
- Для маскировки специфичных зон иерархии можно использовать роль «No Access»
- После перезагрузки и обновления vCenter стоит проверять наличие необходимых прав. Дело в том, что если на каком-то этапе возникли сетевые проблемы и vCenter не сможет верифицировать указанные группы или пользователей, они будут удалены и заменены local\Administrators.
- Удалить права на vCenter для локальной группы Administrators и пользователя Administrator сервера vCenter. Выдать права специализированной группе.
Напоследок упомяну о специализированных пользователях хостов ESXi. Спровоцировано тем, что коллега однажды решил убедиться, что сотрудники ИТ в некоторых регионах не наделали себе лазеек в инфраструктуре, и чуть было не вычистил ESXi-хосты от пользователя vpxuser.
vpxuser — специализированный пользователь, который создаётся при подключении хоста к vCenter и используется им для администрирования. Имеет, соответственно, административные права на хост и ни в коем случае не должен модернизироваться (не менять ни права ни пароль).
dcui user — ещё один специфичный пользователь, используемый в качестве агента при работе через Direct Console User Interface режиме lockdown mode хоста (в этом режиме любые подключения к хосту запрещены, кроме управления с помощью vCenter).
В качестве заключения хочу заметить, что никогда я настолько не осознавал значимости и актуальности AGDLP-подхода при назначении прав доступа к системе, как при разработке политики назначения прав на объекты vCenter. Ввиду вышеприведённых особенностей и большого количества ветвлений элементов иерархий.
VMware ESXi DCUI (Direct Console User Interface)
The first screen after ESXi installation or boot is called ESXi DCUI (Direct Console User Interface). In this blog we will discuss some basic configurations of ESXi using DCUI. Although all the configuration can be done using vSphere Client, vCenter or SSH login but ESXi DCUI is used when there is some network issue in all remote options or in case of first time Static IP Address allocation to management interface.
First of all, just after installing ESXi we see a screen with Yellow and Grey background showing VMware ESXi version, CPU/Memory resources and the link to download the vSphere Client to manage that host in below format:
http://hostname/
http://<IP Address>/
However you can also download the vSphere Client from VMware website (above links will also use the same VMware link to download).
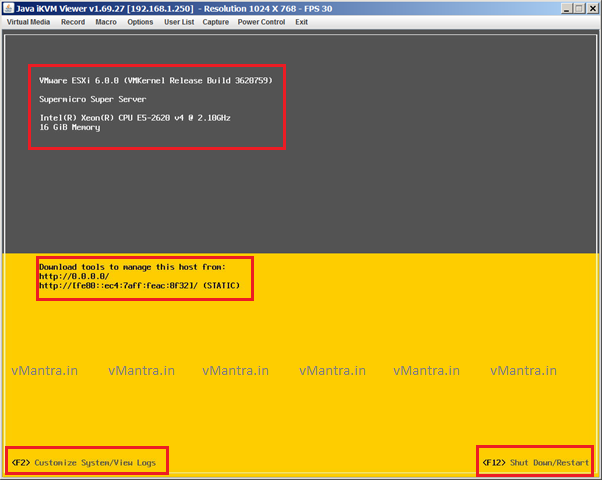
There are only two options available, first “F2” to customize system/view logs and second “F12” to Shut Down/Restart ESXi host. To enter into the configuration page you need to press “F2” then it will ask for User Authentication (by default root user’s credential). Enter the password and it will open the System Customization page.
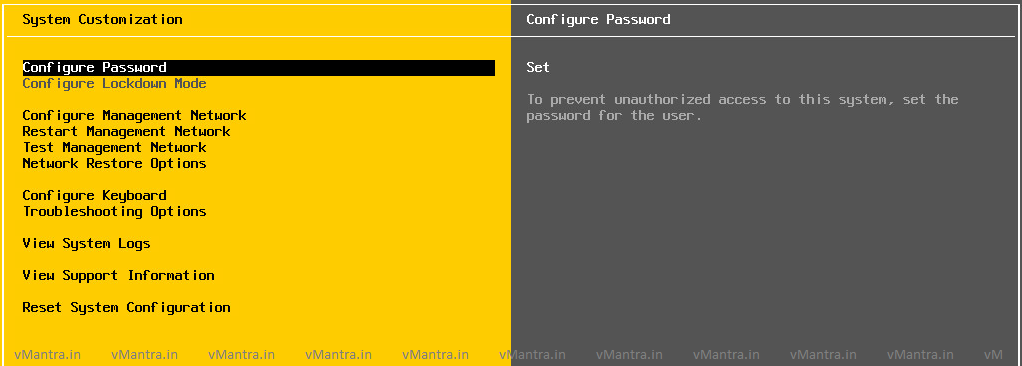
ESXi System Customization:
System Customization page provides the following features:
- Configure Password
- Configure Lockdown Mode
- Configure Management Network
- Restart Management Network
- Test Management Network
- Network Restore Options
- Configure Keyboard
- Troubleshooting Options
- View System Logs
- View Support Information
- Reset System Configuration
Features Details:
Modifying the root password is very simple, just select Configure Password and press Enter. It will ask for Old & New passwords to change the password. Enter the required details then press Enter.
Lockdown Mode is a security feature that prevents user to perform operations against the ESXi host directly. This feature is disabled by-default and only available on ESXi hosts that have been added to vCenter Server.
To configure Hostname, IP Address, DNS use Configure Management Network option and don’t forget to restart the management network as soon as you finished the network configurations. You can also Test the Management Network by entering the IP addresses the Gateway or other servers like NTP.
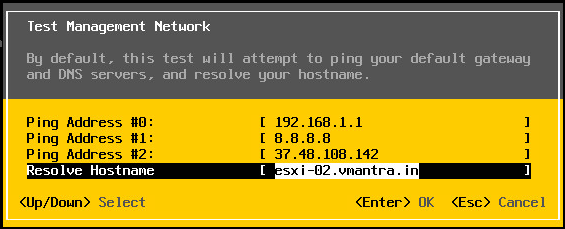
In case of some issue in existing network configuration or you want to change the entire network configuration of ESXi host, VMware ESXi gives you Network Restore options.
If you have chosen the wrong Keyboard layout during ESXi installation, Don’t worry you can change it any time using Configure Keyboard.
Troubleshooting Options facilitates you to enable or disable ESXi Shell and SSH, In addition to that you can also configure the timeouts for Shell, SSH and ESXi DCUI.
You can also see the various system logs along with support information.
And last but not least, if everything seems to be messed up and not under control. At this instant you can factory reset the ESXi hypervisor. As a result it will remove all the configurations including management IP address on ESXi host. But in production environment never ever try to use this option as it may impact your production.
What Is Dcui In Vmware?
The Direct Console User Interface (DCUI) is a menu-based interface that is accessed from the host console and used to configure ESXi running on vSphere hosts.
How do I use DCUI?
After you enable the ESXi Shell in the direct console, you can use these below combination of ALT + Function keys to access the Direct Console User Interface (DCUI) of an ESXi host: ALT+F1 = Switches to the console. ALT+F2 = Switches to the DCUI.
How do I start DCUI?
Select Manage tab and click on Settings and Security Profile. Start Direct Console UI and SSH services. Next step is to simply login via any SSH client to your ESXi host. Simply type dcui in shell and click Enter.
How do I get out of DCUI?
To exit the DCUI, press Ctrl+C.
How do I enable SSH in DCUI?
Enable SSH | DCUI
At the DCUI screen, press F2 to log in. From the System Customization screen, select Troubleshooting Options. Under Troubleshooting Mode Options, choose Enable SSH. SSH will now show Enabled.
What does DCUI stand for?
| Acronym | Definition |
|---|---|
| DCUI | Direct Console User Interface |
| DCUI | Document Centered User Interface |
| DCUI | Data Collection User Interface |
What is VMware lockdown mode?
The Lockdown mode can be used to increase the security of an ESXi host by limiting the access allowed to the host. When this mode is turned on, the ESXi host can only be accesses through vCenter Server or Direct Console User Interface (DCUI).
What is ESXi shell?
The ESXi Shell is an interactive command line environment available locally from the DCUI or remotely via SSH. Activities performed from the ESXi Shell bypass vCenter RBAC and audit controls.
What is vSphere DRS?
VMware vSphere® Distributed Resource Scheduler (DRS) is the resource scheduling and load balancing solution for vSphere. DRS works on a cluster of ESXi hosts and provides resource management capabilities like load balancing and virtual machine (VM) placement.In other words, DRS strives to keep your VMs happy1.
How do I connect to ESXi host?
Follow the steps to log in to the vSphere ESXi Host:
- Open the vSphere Client.
- Enter the IP address or name of the vSphere Hypervisor in the IP address / Name field.
- Enter the user name in the User name field.
- Enter the password in the Password field.
- Click Login.
Where is Esxcli located?
/sbin/ directory
As you see in the console output, ESXCLI is a script written in Python that is located in the /sbin/ directory.
What is Esxcli command?
The ESXCLI command set allows you to run common system administration commands against vSphere systems from an administration server of your choice. The actual list of commands depends on the system that you are running on. Run esxcli –help for a list of commands on your system.
What function key is used to customize server options from the ESXi DCUI?
Using the DCUI to configure an ESXi server
Minimally, you should go in and configure the root username and password as well as static IP network information. To login to the DCUI system customization screen, press F2.
What port does SSH use?
22
Service Name and Transport Protocol Port Number Registry
| Service Name | Port Number | Transport Protocol |
|---|---|---|
| ssh | 22 | tcp |
| ssh | 22 | udp |
| ssh | 22 | sctp |
| sshell | 614 | tcp |
Can agree a key exchange algorithm?
The Couldn’t agree a key exchange algorithm is expected behavior with older version of PuTTy or PuTTy integrated solutions like WInSCP. To resolve this issue, upgrade PuTTy to a version to 0.65 or later from http://www.putty.org/.
What is Vmkfstools?
Vmkfstools is an ESXi Shell command line interface (CLI) for building and managing volumes and virtual disks on an ESX/ESXi host. Among its storage administration features, vmkfstools can be used to copy, convert, rename, import, export and resize virtual disks.
How do I give permission to VMware?
Procedure
- Browse to the object in the vSphere Web Client object navigator.
- Click the Manage tab and select Permissions.
- Click Add Permission.
- Click Add.
- Identify the user or group that will have the permission.
- Select a role from the Assigned Role drop-down menu.
How do I enable ESXi shell?
Use the direct console user interface to enable the ESXi Shell:
- From the Direct Console User Interface, press F2 to access the System Customization menu.
- Select Troubleshooting Options and press Enter.
- From the Troubleshooting Mode Options menu, select Enable ESXi Shell.
- Press Enter to enable the service.
What’s the difference between DC Universe and DC Universe Infinite?
DC today announced the evolution of DC UNIVERSE into DC UNIVERSE INFINITE, a premium digital comic book service set to launch on January 21, 2021.DC’s premium digital comic book platform provides members with an expanded collection of comics and Original Graphic Novels, spanning over 80 years of the DC Multiverse.
What is IPMI in ESXi?
IPMI is a hardware-level specification and Hewlett-Packard iLO is an embedded server management technology. Each of them describes and provides an interface for remotely monitoring and controlling computers.
What is CIM secure server in VMware?
The Common Information Model (CIM) package is available for VMware vSphere 6.5, 6.7 and 7.CIM providers communicate with a CIM client and can be used to achieve such common management use-cases as reporting hardware health monitoring information or updating driver firmware.
Dcui vmware что это
You are using an outdated browser. Please upgrade your browser to improve your experience.
The Direct Console User Interface (DCUI) allows you to interact with the host locally using text-based menus. Evaluate carefully whether the security requirements of your environment support enabling the Direct Console User Interface.
Procedure
- From the Direct Console User Interface, press F2 to access the System Customization menu.
- Select Troubleshooting Options and press Enter.
- From the Troubleshooting Mode Options menu, select a service to enable.
- Enable ESXi Shell
- Enable SSH
- Press Enter to enable the service.
- Press Esc until you return to the main menu of the Direct Console User Interface.
What to do next
Set the availability and idle timeouts for the ESXi Shell . See Set Availability Timeout or Idle Timeout for the ESXi Shell.